
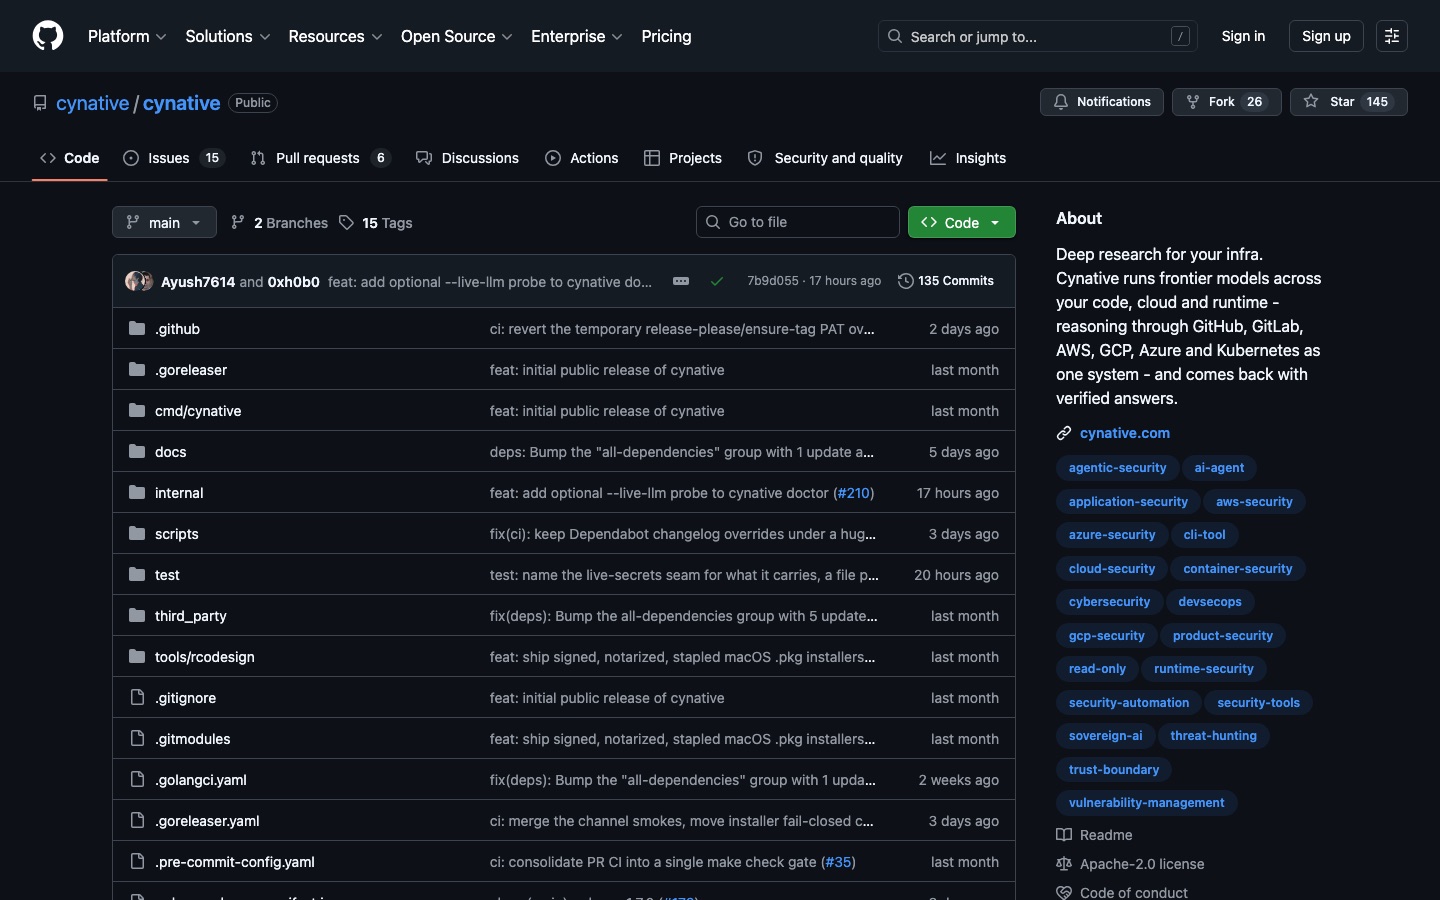
Read-only, fail-closed security research agent for code and cloud infrastructure.
Features
- Multi-cloud and code-platform queries
- Enforced read-only policy
- Pre-call IAM authorization
- Fail-closed security model
- Per-turn JavaScript sandbox
Use Cases
- Cloud security investigations
- Permission and configuration audits
- Repository security research
- Kubernetes risk analysis
FAQ
Read-only, fail-closed security research agent for code and cloud infrastructure. Core capabilities include: Multi-cloud and code-platform queries, Enforced read-only policy, Pre-call IAM authorization.
Common scenarios include: Cloud security investigations, Permission and configuration audits, Repository security research.
